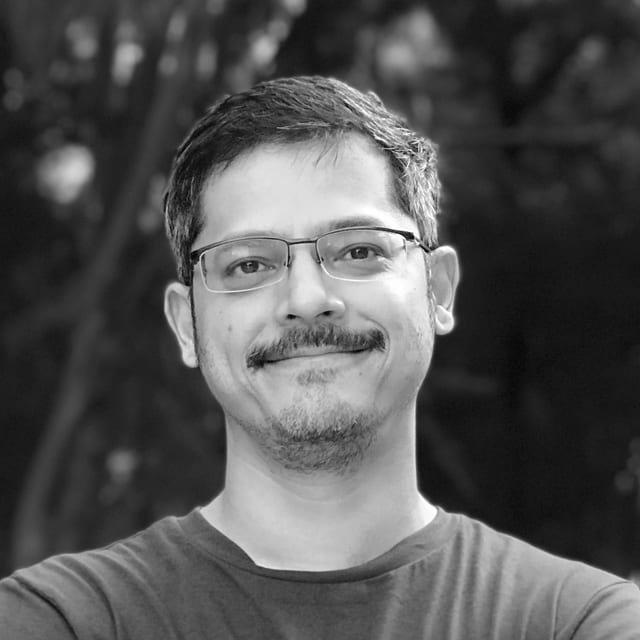
Sandeep Karnik

Sandeep Karnik

Offensive Security & Malware Research
Founder, PalaviTech

My work spans adversary simulation, detection engineering, malware analysis, Active Directory red teaming, EDR, AWS security, infrastructure engineering, and cloud architecture - and the messy space where they all collide.

BytesCop is where I turn that experience into hands-on learning.

Pune, Maharashtra, India
Connect on LinkedIn
At a glance
Offensive security
web, mobile, AD, EDR
Malware research
analysis & ethical development
AWS Cloud Architect
HA, DR, governance, IaC
25+ years
enterprise IT, incl. Microsoft
US · Europe · India
MNC & Fortune 500 programmes
Building, breaking, and defending systems in the age of AI

I'm Sandeep Karnik - the creator of BytesCop and founder of PalaviTech, a cybersecurity firm working in malware analysis, adversary simulation and defensive tooling. My work spans reverse-engineering malware samples and developing controlled payloads to test what EDR solutions actually detect, through to penetration testing of web applications, mobile apps and Active Directory - with reporting that goes beyond identifying vulnerabilities to clearly defining how they should be remediated.

The other half of my background is more than 25 years in enterprise IT, including experience with Microsoft Corporation and programmes for MNCs and Fortune 500 companies across the US, Europe and India. I've also built an AWS cloud architecture practice focused on high availability, disaster recovery, data protection and governance, with infrastructure managed as code.

That combination shapes how I approach security. Understanding how systems are designed, deployed and operated - from IAM models and trust boundaries to logging and data pipelines - provides important context for understanding how they behave when subjected to attack. BytesCop brings these two perspectives together: the mindset of understanding how systems can be tested and challenged, with the practical knowledge of how they are built and secured in the first place.

Red team. Blue team. Hands on.
Commands, not summaries
Tutorials carry the actual invocation, the actual output, and what to look at in it.
Down to the primitive
Articles go past the vendor headline to the mechanism a technique actually abuses.
Labs you work yourself
Reproducible environments, so the exercise is doing it rather than watching it.
From engagements, not slide decks
Every technique here comes out of client work delivered on real systems, offensive or defensive.
Ethical first
Offensive technique taught for defenders, in controlled labs, with rules of engagement treated as part of the craft.
In other people's words
verify on LinkedIn

I've had the privilege of working with Sandeep Karnik over the past few years, and he consistently stands out as one of the strongest penetration testing and ethical hacking professionals I've collaborated with. His combination of deep technical expertise and highly practical, real-world thinking means he doesn't just find vulnerabilities - he explains the real risk, prioritizes what matters, and helps teams actually fix them. Sandeep is thorough in his methodology, and exceptionally reliable when dealing with complex, business-critical security assessments. I would confidently recommend Sandeep for any organization looking for a trusted, top-tier expert to lead or execute penetration testing and ethical hacking projects.
Mobin Muhammed
Mobin Muhammed
Worked with Sandeep on the same team · November 2025

Sandeep & I worked together at Microsoft's Dynamics Division in Denmark during transition of its on-premise products to their 3-tier cloud ready equivalents. Sandeep is a skilled technical architect in cloud and solution architecture space - someone who is a fast learner, go-getter, persistent, problem solver with out of the box creative thinking combined with innovative and contemporary techniques.
Naveen Garg
Naveen Garg
Co-founder, Product & Technology Chief - BizSchoolie
Worked with Sandeep on the same team · April 2022

Sandeep is our window to the future. Always 10 steps ahead of us. We have benefitted immensely from his constant hunger to share and teach new things in the IT-sphere. Holding his finger offers us the confidence to step ahead.
Niranjan Deshpande
Niranjan Deshpande
Kisan Forum
Sandeep's client · April 2022

Sandeep has a great mind to combine understanding for customer needs and features on one side and the technical implications on the other. When adding all the hard work Sandeep did in our team I was a true pleasure to work with him.
Michael Englev
Michael Englev
Software test management & DevOps leadership, Copenhagen
Managed Sandeep directly · April 2022
Malware analysis & reverse engineering
Static triage through to sandbox detonation and memory forensics - unpacking binaries, recovering decrypted configs, and mapping persistence and evasion to MITRE ATT&CK.
Adversary simulation
Red-team operations against real tradecraft: initial access, persistence, privilege escalation, defence evasion and C2, run in phases against live telemetry.
Ethical malware development
Controlled loaders, payloads and beacons built to benchmark EDR and AV - obfuscation, LOLBins, API unhooking and indirect syscalls, all environment-bound with kill-switches.
Active Directory & identity
Attack-path mapping across AD and hybrid Entra ID - Kerberoasting, DCSync, delegation abuse, ticket replay, stale trusts, LLMNR and NTLM relay.
Detection engineering
YARA, Sigma and Suricata content, threat-hunting queries and IR playbooks on Elastic Stack and Amazon OpenSearch - ingestion, enrichment, correlation and alerting that cuts MTTR instead of noise.
Phishing & human risk
Authorised email, spear-phishing and BEC campaigns measuring click-through, credential submission and reporting behaviour - then closing the gap with targeted training.
Cloud security & architecture
AWS security and architecture audits - IAM, network segmentation, logging and monitoring, threat detection, encryption and key management, backup posture and incident readiness - plus the resilient platforms themselves.
Security tooling & hardening
Building the instruments: C++ enumeration tooling for Windows and AD, Django/Angular security platforms, and hardened Linux baselines across Ubuntu and RHEL, automated with Ansible.
ToolboxMITRE ATT&CKYARASigmaSuricataElastic StackAmazon OpenSearchActive DirectoryEntra IDAWSInfrastructure as codeAnsibleDockerDocker SwarmC++PowerShellDjangoAngularUbuntuCentOS / RHELCI/CD
Selected work
Adversary Simulation & Red Teaming
Emulating real-world attackers across the kill chain - from initial access and execution to persistence, lateral movement, privilege escalation, and objective-driven operations.
Detection Engineering & EDR
Turning offensive tradecraft into better detection. Building and validating detections across EDR, SIEM, network telemetry, and endpoint controls through controlled adversary activity.
Malware Analysis & Reverse Engineering
Taking apart malicious binaries to understand what they do, how they operate, and how to detect them - from static PE analysis and API behavior to runtime execution and capability mapping.
Windows, Active Directory & Identity Security
Going deep on the Windows security model - authentication, Kerberos, AD attack paths, privilege escalation, lateral movement, persistence, and the controls that stop them.
AWS Security & Cloud Architecture
Designing and assessing AWS environments with security built into the architecture - IAM, networking, workload isolation, logging, detection, encryption, resilience, and multi-account strategy.
Infrastructure Engineering
Building the infrastructure security actually depends on - networks, Linux and Windows servers, firewalls, VPNs, segmentation, hardening, automation, and production operations.
Security Architecture & Engineering
Bridging security requirements with systems that have to work in the real world. Designing secure platforms, reviewing architectures, identifying attack paths, and turning findings into practical engineering decisions.
Automation, Tooling & Security Engineering
Writing the tools that make security work faster and repeatable - Python, C/C++, Windows APIs, AWS automation, security tooling, analysis frameworks, and custom research utilities.
Latest bits
BytesCop Reporter
An open-source, self-hosted platform consolidating pen tests, scans and manual assessments into one auditable source of truth - multi-tenant isolation, TOTP MFA, RBAC and an append-only audit trail, on Django, Angular and Docker.
palavitech/bytescop-reporter
PalaviTech ShieldPRE-RELEASE
A C++ console application that enumerates Windows machines, networks and Active Directory for misconfigurations, weak protocols and update drift - built for the sysadmins who have to fix them.
Career
Founder · Pune, India
Current
Microsoft Corporation
Enterprise IT
Earlier roles
Copenhagen, Denmark · Mumbai, India · enterprise programmes across the US, Europe and India
Recognition
Surpass Award
Recognised for performance
Best Techy in Microsoft Technology
Nominated
Education
University of Mumbai
1990 - 1995
Your PC Is Acting Weird… Can You Find the RAT Before It's Too Late?
VideoJun 12, 2026
Your PC Is Acting Weird… Can You Find the RAT Before It's Too Late?

No EDR, no alerts, no clue - a live hunt for a RAT hiding in plain sight on a Windows box, tracked down with Sysinternals Process Explorer.

Watch on YouTube →
ArticleMar 30, 2026 · 19 min read
Understanding NTFS Permission Inheritance and Reading icacls Output

A practical guide to NTFS inheritance flags (CI, OI, IO, NP, I) - what each flag means, how they combine, how to read real icacls output, and twelve common misconfiguration mistakes that lead to security issues.

windows securityntfsaccess controlsysadmin
Read article →
ArticleMar 28, 2026 · 6 min read
Anatomy of a Malware Dropper: Static and Dynamic Analysis Walkthrough

A step-by-step teardown of a real-world malware dropper - from PE header analysis and string extraction through sandbox execution, IOC extraction, MITRE ATT&CK mapping, and YARA rule creation.

malware analysisreverse engineeringyara
Read article →
ArticleMar 21, 2026 · 7 min read
5 Active Directory Attack Paths We Find in Every Engagement

Kerberoasting, DCSync, unconstrained delegation, NTLM relay, and credential spraying - how each attack works, what defenders see in logs, and concrete steps to remediate.

active directoryred teamdefense
Read article →
ArticleMar 14, 2026 · 8 min read
Building Detection Rules That Actually Fire: A Sigma Rule Development Guide

How to write Sigma detection rules that catch real attacks without drowning your SOC in false positives - with five production-ready rules, SIEM conversion examples, and a tuning methodology.

detection engineeringsigmasiem
Read article →
Learn with meNOW LIVE

More in development, on malware analysis, adversary simulation and detection engineering - drawn from engagements, not textbooks.
Work with me
Adversary simulation & red team
Penetration testing
Malware analysis & detection content
Phishing simulation & awareness
AWS security & architecture audits
Corporate training & workshops
contact@palavi.tech Message on LinkedIn
Display Mode
Direction Mode
Theme Color
Theme Cover